
Disclaimer: The opinions expressed by our writers are their own and do not represent the views of U.Today. The financial and market information provided on U.Today is intended for informational purposes only. U.Today is not liable for any financial losses incurred while trading cryptocurrencies. Conduct your own research by contacting financial experts before making any investment decisions. We believe that all content is accurate as of the date of publication, but certain offers mentioned may no longer be available.
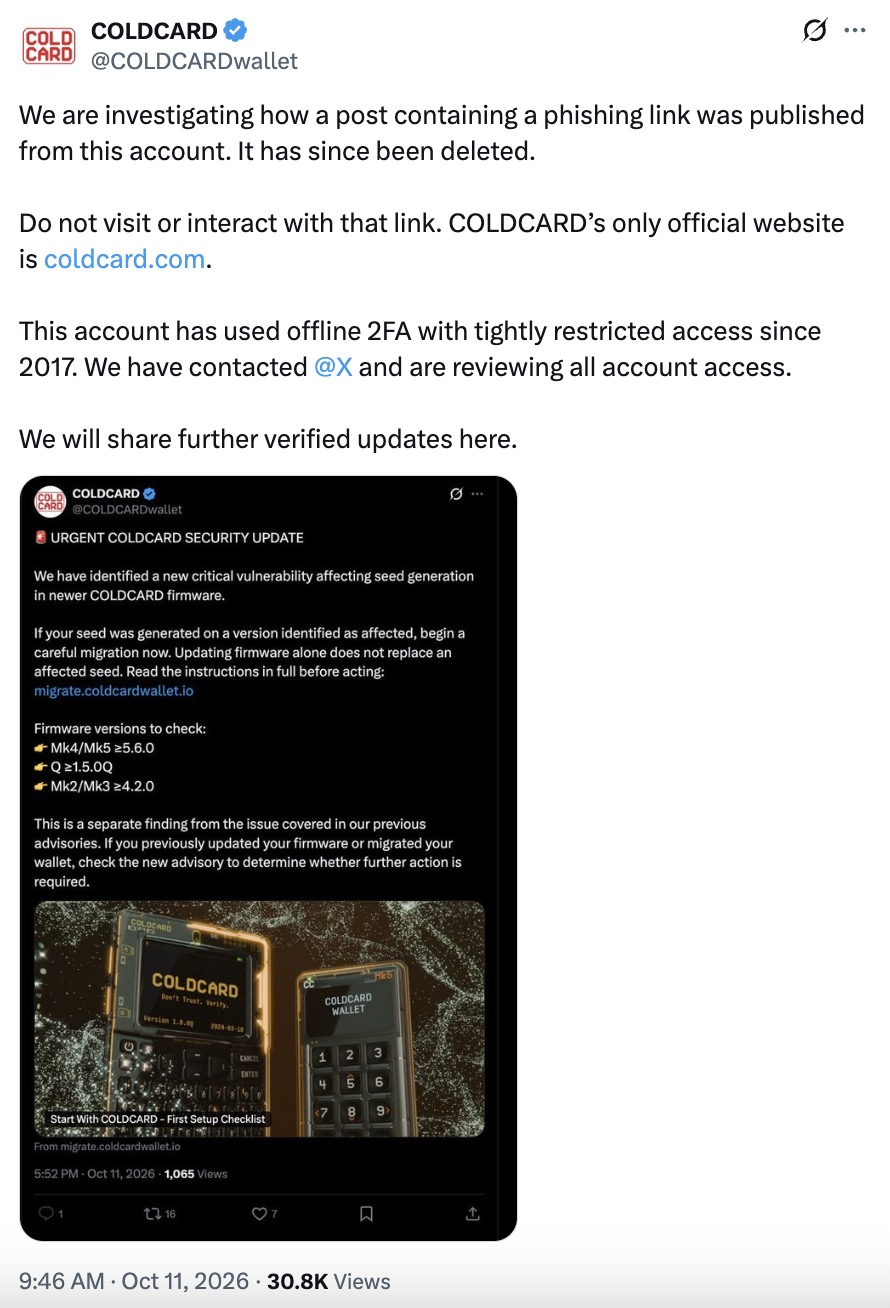
The official X account of Bitcoin hardware wallet manufacturer Coldcard was compromised. On October 11, 2026, attackers published a fake notice in the brand’s name claiming a “critical firmware vulnerability” affecting the Mk4, Mk5, and Q models and urging users to move their funds immediately through a phishing website.

The post appeared amid unprecedented anxiety in the crypto community. Hackers exploited the context of the brand’s recent disaster to make the scam more convincing. The post was subsequently deleted.
Why the fake notice was so convincing
The reason is that Coldcard experienced the biggest crisis in its history in late July 2026. Due to a linker error in the device code, wallets were generated with weak entropy (randomness). Instead of using a true random number generator (TRNG), the system relied on a vulnerable software algorithm. Hackers cracked the wallets offline through brute-force attacks and drained the addresses without any phishing.
The first wave of thefts began on July 30, 2026, with total losses estimated at around 1,600–1,800 BTC (approximately $100–130 million at the time), making it one of the year's largest self-custody incidents.
Coinkite, the wallet manufacturer, responded by urgently releasing patched firmware versions: 4.2.0 for Mk3, 5.6.0 for Mk4/Mk5, and 1.5.0Q for Q. However, the software update did not automatically fix existing wallets. Users had to manually generate new seed phrases and migrate their assets.
This painful procedure was precisely what the scammers mimicked on October 11. They listed exactly the same “patched” firmware versions in their phishing post to trigger panic and encourage users to transfer their funds to the attackers’ addresses.
The intrigue surrounding the latest incident is that Coldcard representatives found absolutely no evidence of a breach in their own systems. The company stated that its logs contained no records of unauthorized logins or sessions, and that its own credentials and offline two-factor authentication (2FA) method, which has been used since 2017, remained secure.
The Coldcard team officially contacted X support, demanding an urgent investigation. According to the company, the post bypassed its security measures through unauthorized access at the social network level or via its administrative panel.
The developers also cited reports of access to X's internal tools being sold on dark markets, although no independent evidence has yet confirmed a connection. The risk of losing funds likely applies only to users who panicked and manually entered their 24-word seed phrases on the phishing page.
 Arman Shirinyan
 Dan Burgin