
Disclaimer: The opinions expressed by our writers are their own and do not represent the views of U.Today. The financial and market information provided on U.Today is intended for informational purposes only. U.Today is not liable for any financial losses incurred while trading cryptocurrencies. Conduct your own research by contacting financial experts before making any investment decisions. We believe that all content is accurate as of the date of publication, but certain offers mentioned may no longer be available.
Developers using Claude AI through Visual Studio Code (VS Code) may have been exposed to a serious security threat after researchers discovered a malicious version of the popular coding assistant's extension.
According to an October 30 report from cybersecurity researchers at OpenSourceMalware, version 2.1.313 of the Claude Code extension contained a hidden backdoor that could enable attackers to remotely access infected computers.
The malicious version was identified in the Open VSX extension registry, where developers download tools for their coding environments.
A Hidden Backdoor in a Trusted AI Tool
The compromised extension reportedly looked and functioned like the legitimate Claude Code tool, making the threat particularly difficult to notice. However, researchers discovered additional malicious code designed to run automatically when the extension loaded.
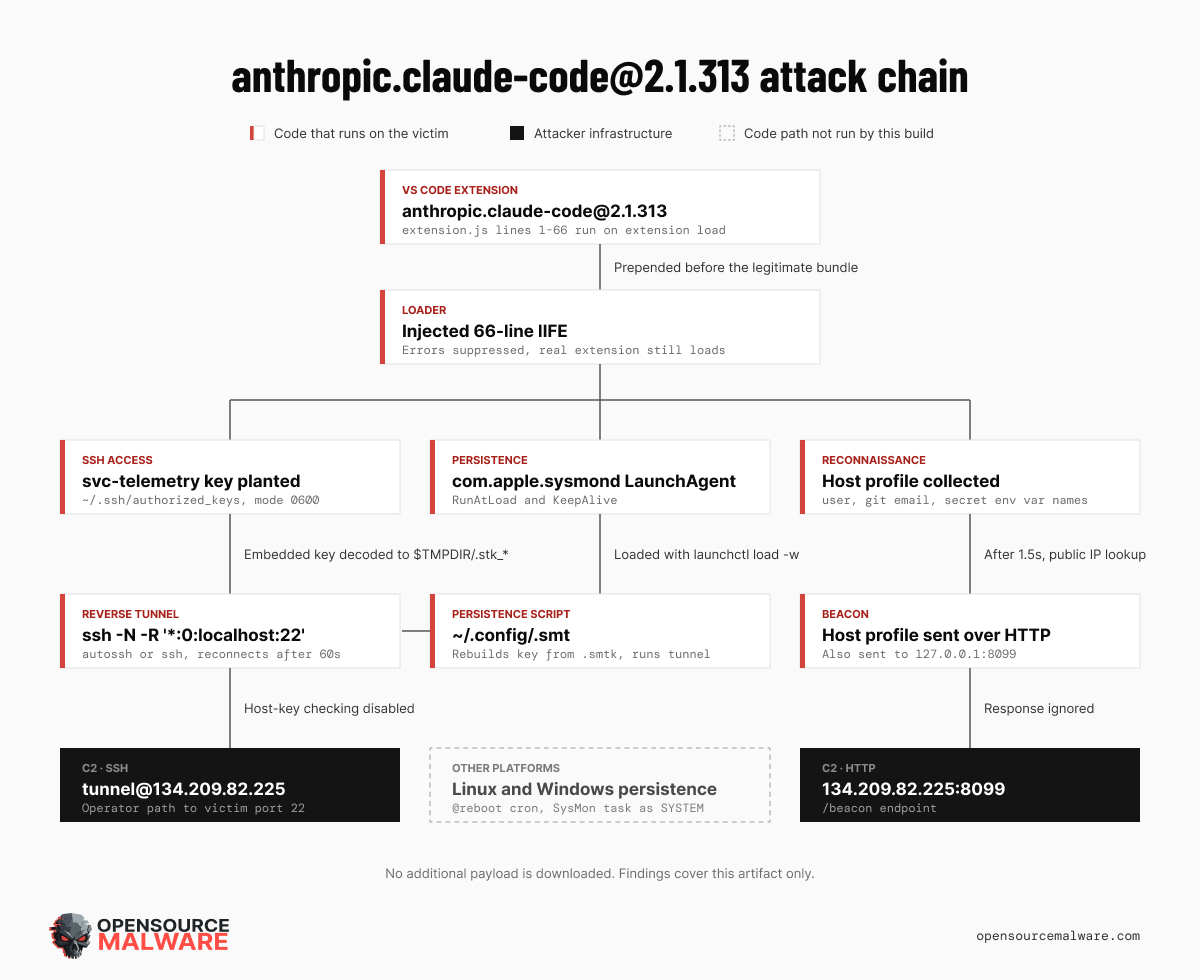
Once activated, the backdoor attempted to establish a remote connection to an attacker-controlled server, potentially giving hackers access to the victim's computer.
More concerningly, the malware was designed to remain active even after the computer restarted.
This means simply closing VS Code or stopping work with Claude might not eliminate the threat.
Why Crypto Developers Should Pay Attention
Although the attack was not specifically designed to target cryptocurrency users, developers working on blockchain projects could face significant risks.
Their computers may contain sensitive information, including private keys, wallet credentials, exchange API keys, and access to cryptocurrency infrastructure.

If attackers successfully gained remote access, they could potentially obtain this information and use it to compromise wallets or projects.
However, researchers did not report confirmed cryptocurrency theft or identify any specific blockchain-related functionality in the malicious code.
Was Anthropic's Official Extension Compromised?
The researchers confirmed malicious code in the analyzed Open VSX version but could not establish how it was introduced.
Importantly, the findings do not prove that Anthropic's official VS Code Marketplace release or its broader distribution systems were compromised.
Developers who installed version 2.1.313 through Open VSX should treat their systems as potentially compromised and investigate immediately.
Removing the extension alone may not be sufficient, as the backdoor was designed to persist independently.
 Arman Shirinyan
 Dan Burgin